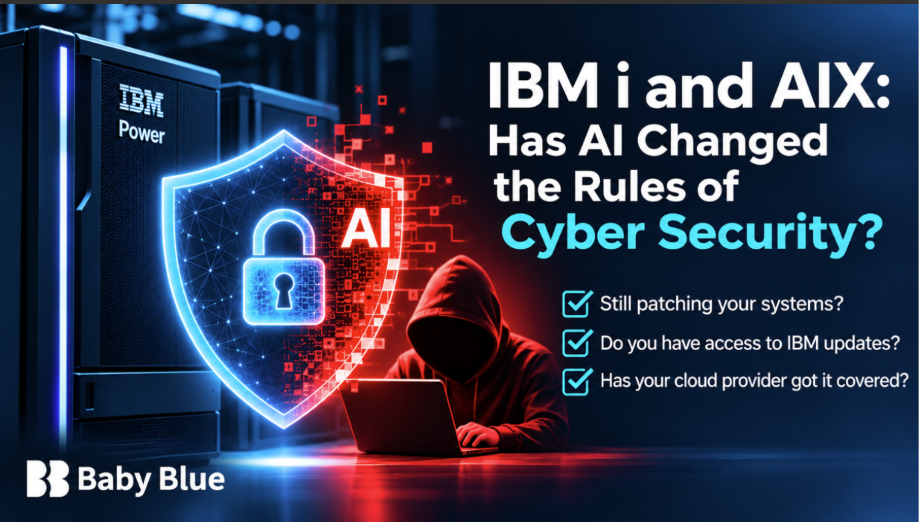
IBM i and AIX: Has AI Changed the Rules of Cyber Security?
16 November 2026 - 5 Minute Read
IBM i and AIX have long been considered among the most reliable and secure enterprise platforms. But could artificial intelligence be changing the risks for systems traditionally regarded as almost untouchable?
Whether you own and operate your IBM Power systems, run your IBM i or AIX workloads through a cloud provider, have lost access to IBM updates, or simply haven't given patching much thought because your systems have always worked, these emerging risks apply to you.
Your systems may be running perfectly, but that doesn't necessarily mean they're receiving the latest security patches, firmware and machine code updates.
The platforms that just keep running
IBM i and AIX have earned their reputation for exceptional reliability. These are the platforms that quietly run business-critical applications for years, often with very little intervention.
They're frequently described as bombproof.
Historically, this reputation has meant they haven't always received the same rigorous patching and security attention as more mainstream platforms.
There was also a perception that their specialist nature offered protection. Successfully attacking these systems required considerable technical knowledge, and the relatively small community of experts was largely made up of passionate advocates for the technology.
When systems worked reliably, there was little appetite to interfere.
If it isn't broken, why fix it?
AI is changing the threat landscape
Traditionally, sophisticated hackers needed extensive technical expertise to identify vulnerabilities and develop attacks.
Artificial intelligence is beginning to change that.
AI tools can assist with analysing code, identifying vulnerabilities and developing attack techniques, reducing the knowledge and effort previously required.
This doesn't mean anyone can suddenly hack an IBM i or AIX system, but the technical barriers that once made specialist platforms less attractive targets are becoming lower.
The UK's National Cyber Security Centre (NCSC) has highlighted how AI is accelerating vulnerability discovery and exploitation, creating new challenges for organisations managing legacy technology.
The platforms haven't become less reliable. The threats around them are evolving.
When was your IBM Power environment last patched?
Many IBM i and AIX environments continue running perfectly while accumulating years of outstanding operating system updates, PTFs, firmware and machine code fixes.
Sometimes this is because organisations are reluctant to disturb stable systems. Sometimes experienced specialists have retired or moved on.
In other cases, organisations have moved away from IBM maintenance and no longer have the entitlements required to access updates.
Whatever the reason, a system that runs flawlessly isn't necessarily a system that's secure.
As AI makes vulnerability research more accessible, relying on obscurity and specialist knowledge is becoming an increasingly risky strategy.
That doesn't mean applying every update immediately. Business-critical environments require careful assessment, compatibility testing and controlled implementation.
But organisations should understand what updates are missing, the risks they represent and whether they have the means to address them.
In the cloud? Don't assume you're protected
Moving IBM i or AIX workloads into the cloud doesn't automatically guarantee that operating systems, firmware and security updates are being maintained.
Responsibilities vary between providers, and some may focus on infrastructure availability rather than keeping every component fully patched.
Even with a managed service, organisations should independently verify the current state of their environment rather than assume their provider is keeping everything up to date.
Outsourcing the management of your systems doesn't mean outsourcing accountability for their security.
An independent health check can establish what's actually being maintained, identify outstanding updates and highlight gaps between expectations and reality.
How Baby Blue can help
At Baby Blue IT & Consulting, we help organisations maintain secure, reliable and cost-effective IBM Power environments, whether on-premise or in the cloud.
We can help you:
- Identify potential risks through independent IBM i and AIX health checks covering operating system levels, PTFs, firmware and maintenance status.
- Regain access to IBM updates by exploring reinstatement of IBM hardware and software maintenance, potentially without historical reinstatement penalties.
·Apply updates safely using our experienced IBM Professional Services specialists to assess compatibility, plan maintenance windows, implement the necessary updates and validate systems afterwards.
- Optimise maintenance costs by combining IBM and third-party support where appropriate, without compromising essential update entitlements.
We don't believe in upgrading systems simply for the sake of it. We believe in understanding the risks and finding the most practical, cost-effective solution.
The systems haven't changed. The threats have.
IBM i and AIX remain exceptional enterprise platforms, but the security assumptions of ten or twenty years ago deserve another look.
AI is making sophisticated cyber capabilities more accessible, and systems that have historically received little security attention may now warrant closer scrutiny.
Your IBM Power systems may still be bombproof when it comes to reliability. But when was the last time you checked their security?
Whether you need an independent security and maintenance review, specialist help applying updates, or have moved to third-party maintenance and need to regain access to IBM fixes, Baby Blue can help.
We work with IBM to identify the most cost-effective route back to IBM support, including opportunities to reinstate maintenance without historical penalties. We can also combine IBM and third-party maintenance where appropriate, ensuring you have access to essential updates without paying more than necessary.
Contact Baby Blue IT & Consulting to request a quotation for an independent IBM Power review, specialist patching assistance or a cost-effective return to IBM support.
About the Author
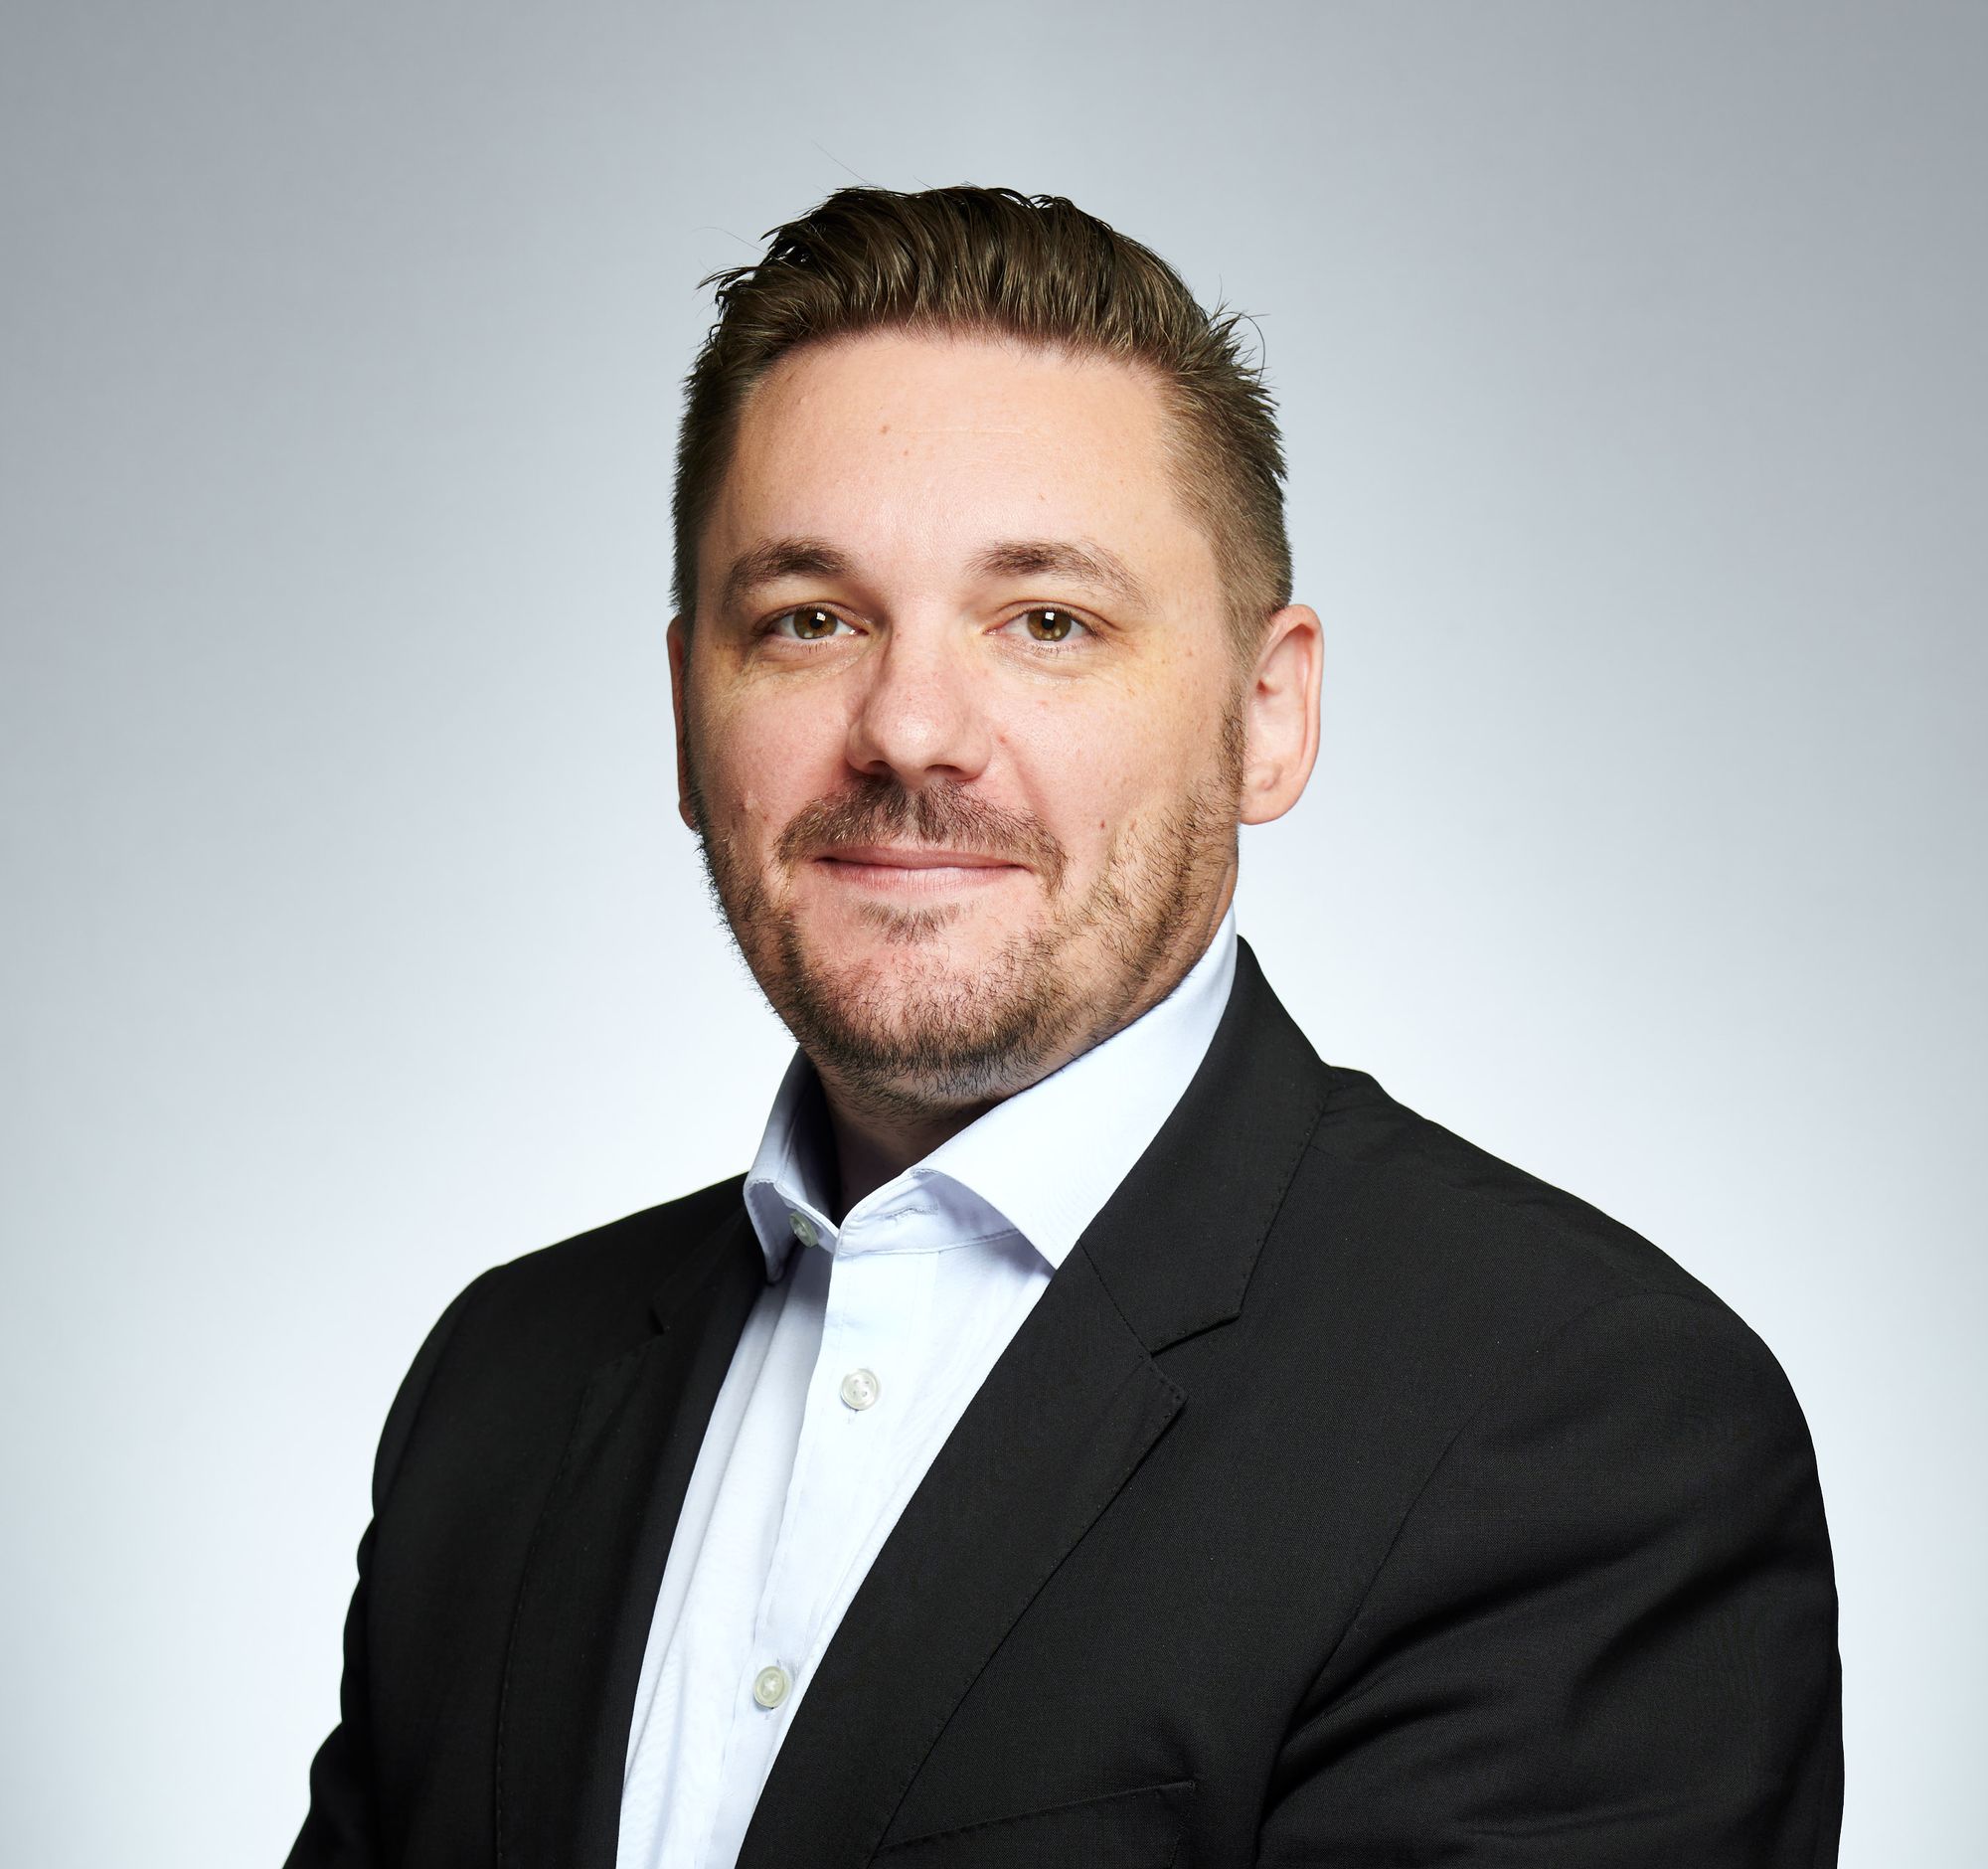
Chris Smith
Chris Smith is a Non-Executive Director and commercial advisor with over 30 years’ experience in IT services across managed services (MSP) and third-party maintenance (TPM). With a background in IBM hardware maintenance, he progressed from field engineer to Sales & Marketing Director, helping to create the foundations of Blue Chip Cloud, which became the largest IBM Power Cloud globally at the time. He played a key role in the sale of Blue Chip in 2021 and subsequently led commercial growth and integration initiatives within Service Express, including delivering significant managed services growth and strengthening revenue predictability. Chris now works with private equity-backed, investor-led and founder-owned IT services businesses, supporting growth, commercial strategy, integration and exit readiness. He is particularly focused on helping organisations improve revenue quality, margin discipline and scalable go-to-market execution across MSP and TPM models.
LinkedIn